Microsoft Finally Lets AI Agents Call Home
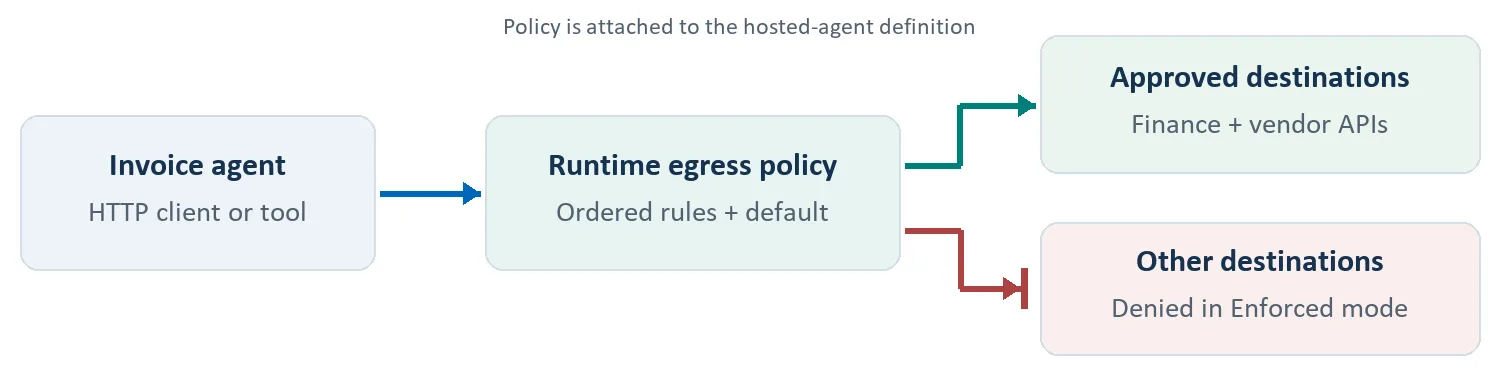
Microsoft Foundry Agent Service has introduced network egress controls, allowing developers to define outbound policies, monitor calls in Audit, and strictly enforce allowed and denied destinations for hosted agents.
- Admins can now stop rogue AI agents from wandering off to unauthorized servers on the public internet.
- Audit mode provides visibility into where your hosted agents actually want to connect before you enforce the rules.
- It is a necessary corporate leash for automated systems that otherwise love downloading random files.
Why should I care? Could be big
Basic perimeter security for AI agents is finally arriving, though it should have been there on day one.
Read the original: Control where your hosted agent connects with network egress in Foundry Agent Service